One-time-code vault
Your two-factor codes inside Odoo, tied to the client and the mandate, on a server that cannot read them.
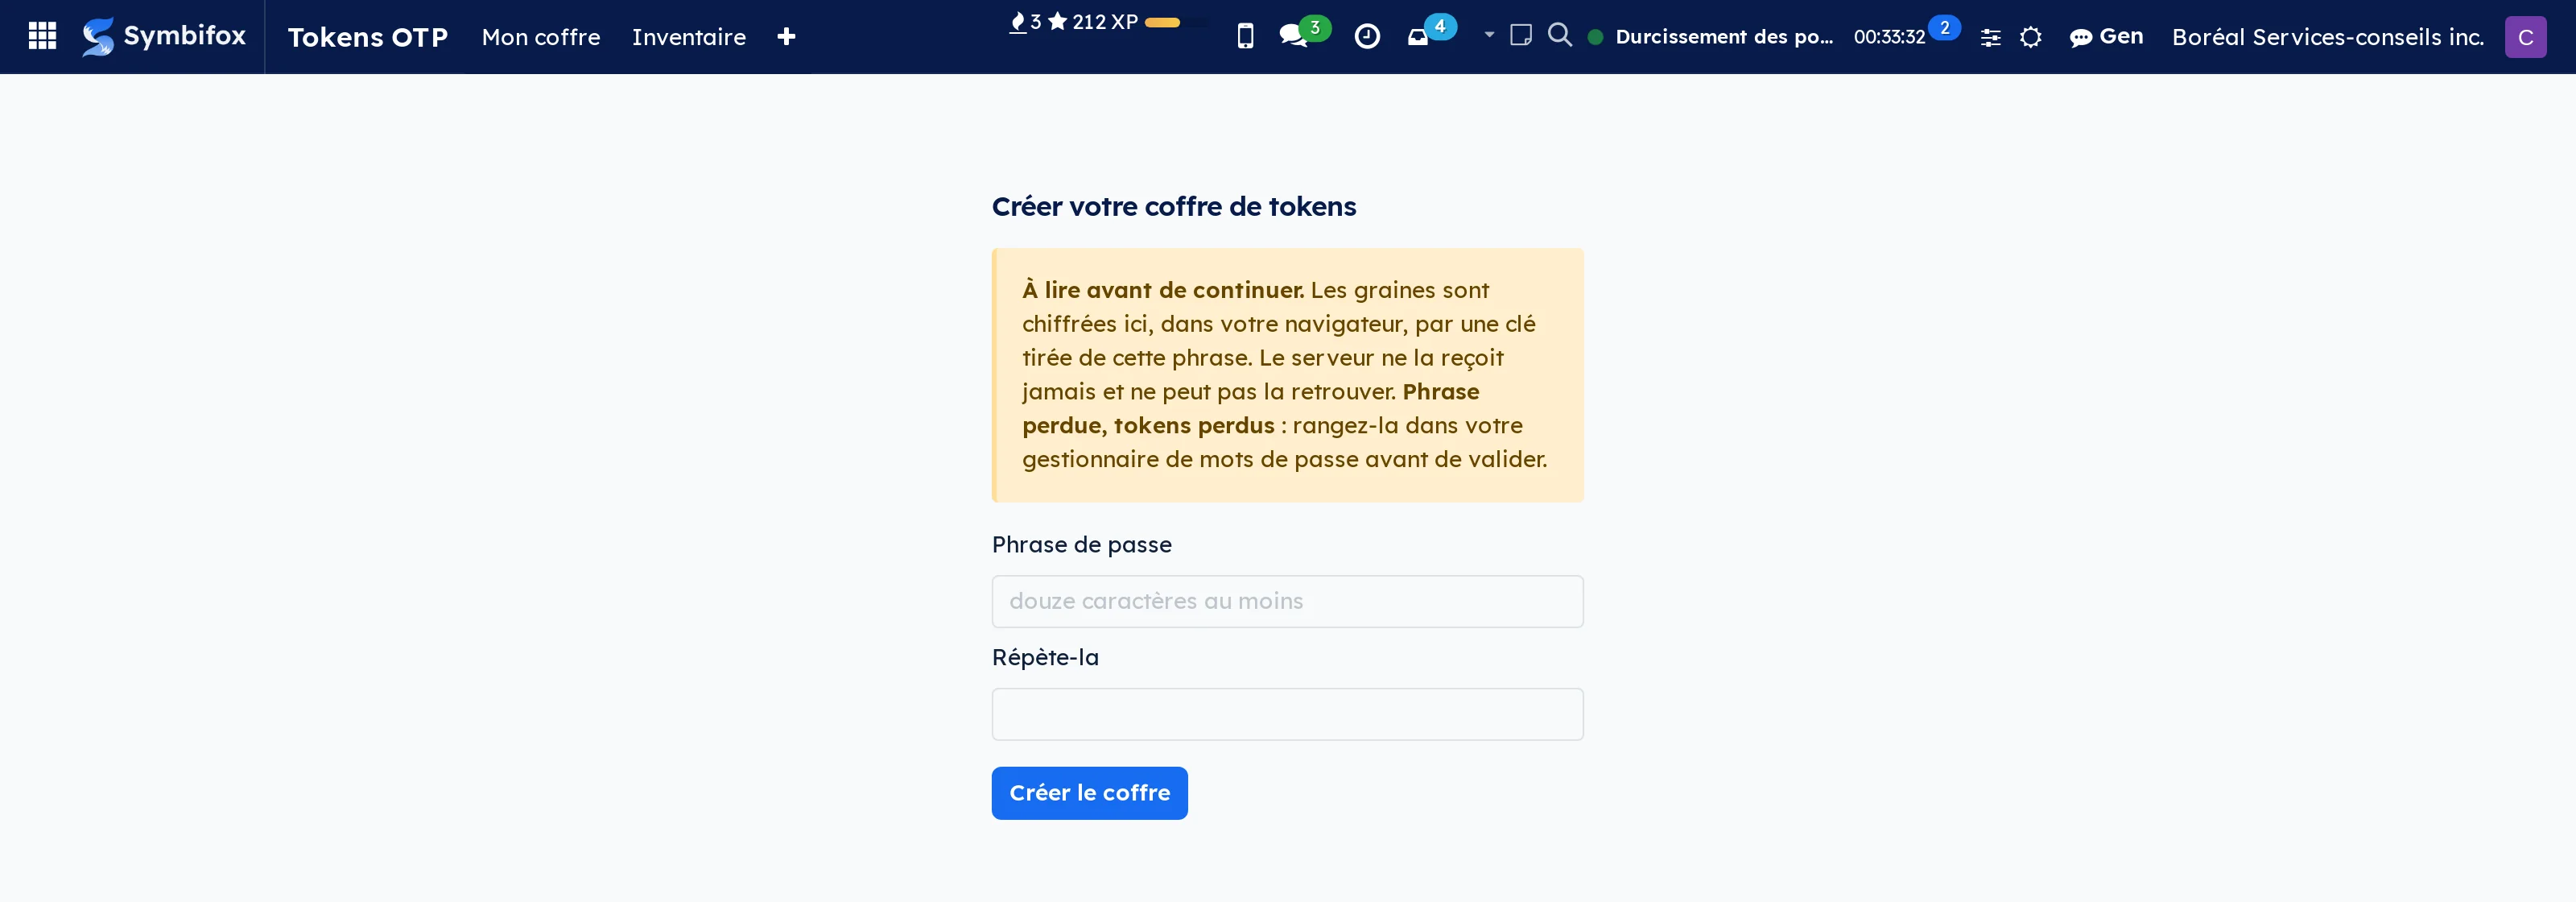
A team's one-time codes live on somebody's phone. Nobody knows what is held for whom, and a departure is discovered on the day someone needs to get in. This module puts the vault in Odoo, every code tied to its client and its mandate, and the client record says how many you hold for them.
The property it buys is rarer than the feature: the server holds no readable seed. Encryption happens in your browser, the key is derived from a passphrase that never leaves it, and the codes are computed in the page. We cannot produce your codes, and that is not a promise: it is checkable in the published source.
Open it with a fingerprint or a hardware key, and keep a recovery code offline for the day the passphrase is lost. The archive takes what you use twice a year out of the everyday list without destroying anything: the code still lives there, and search finds it. An assistant reads the domain in your accounts and proposes a filing for a whole vault, which you correct before it writes.
⚠️ And you are locked in nowhere: the encrypted export is the default, a plain export sits behind your passphrase, with one otpauth:// address per code that any other manager can read back.
Shall we look at your case together?
Tell us what you run today. We will tell you honestly whether Symbifox helps or not.
The catalog grows almost every month.
What gets added, what we learn deploying it, and nothing else. You leave whenever you want.
One confirmation email, and nothing before you follow its link. Then 10 welcome emails, one a week, then the updates. No tracker, no resale.