IT Audit
Structured IT security audits for Quebec Law 25 compliance.
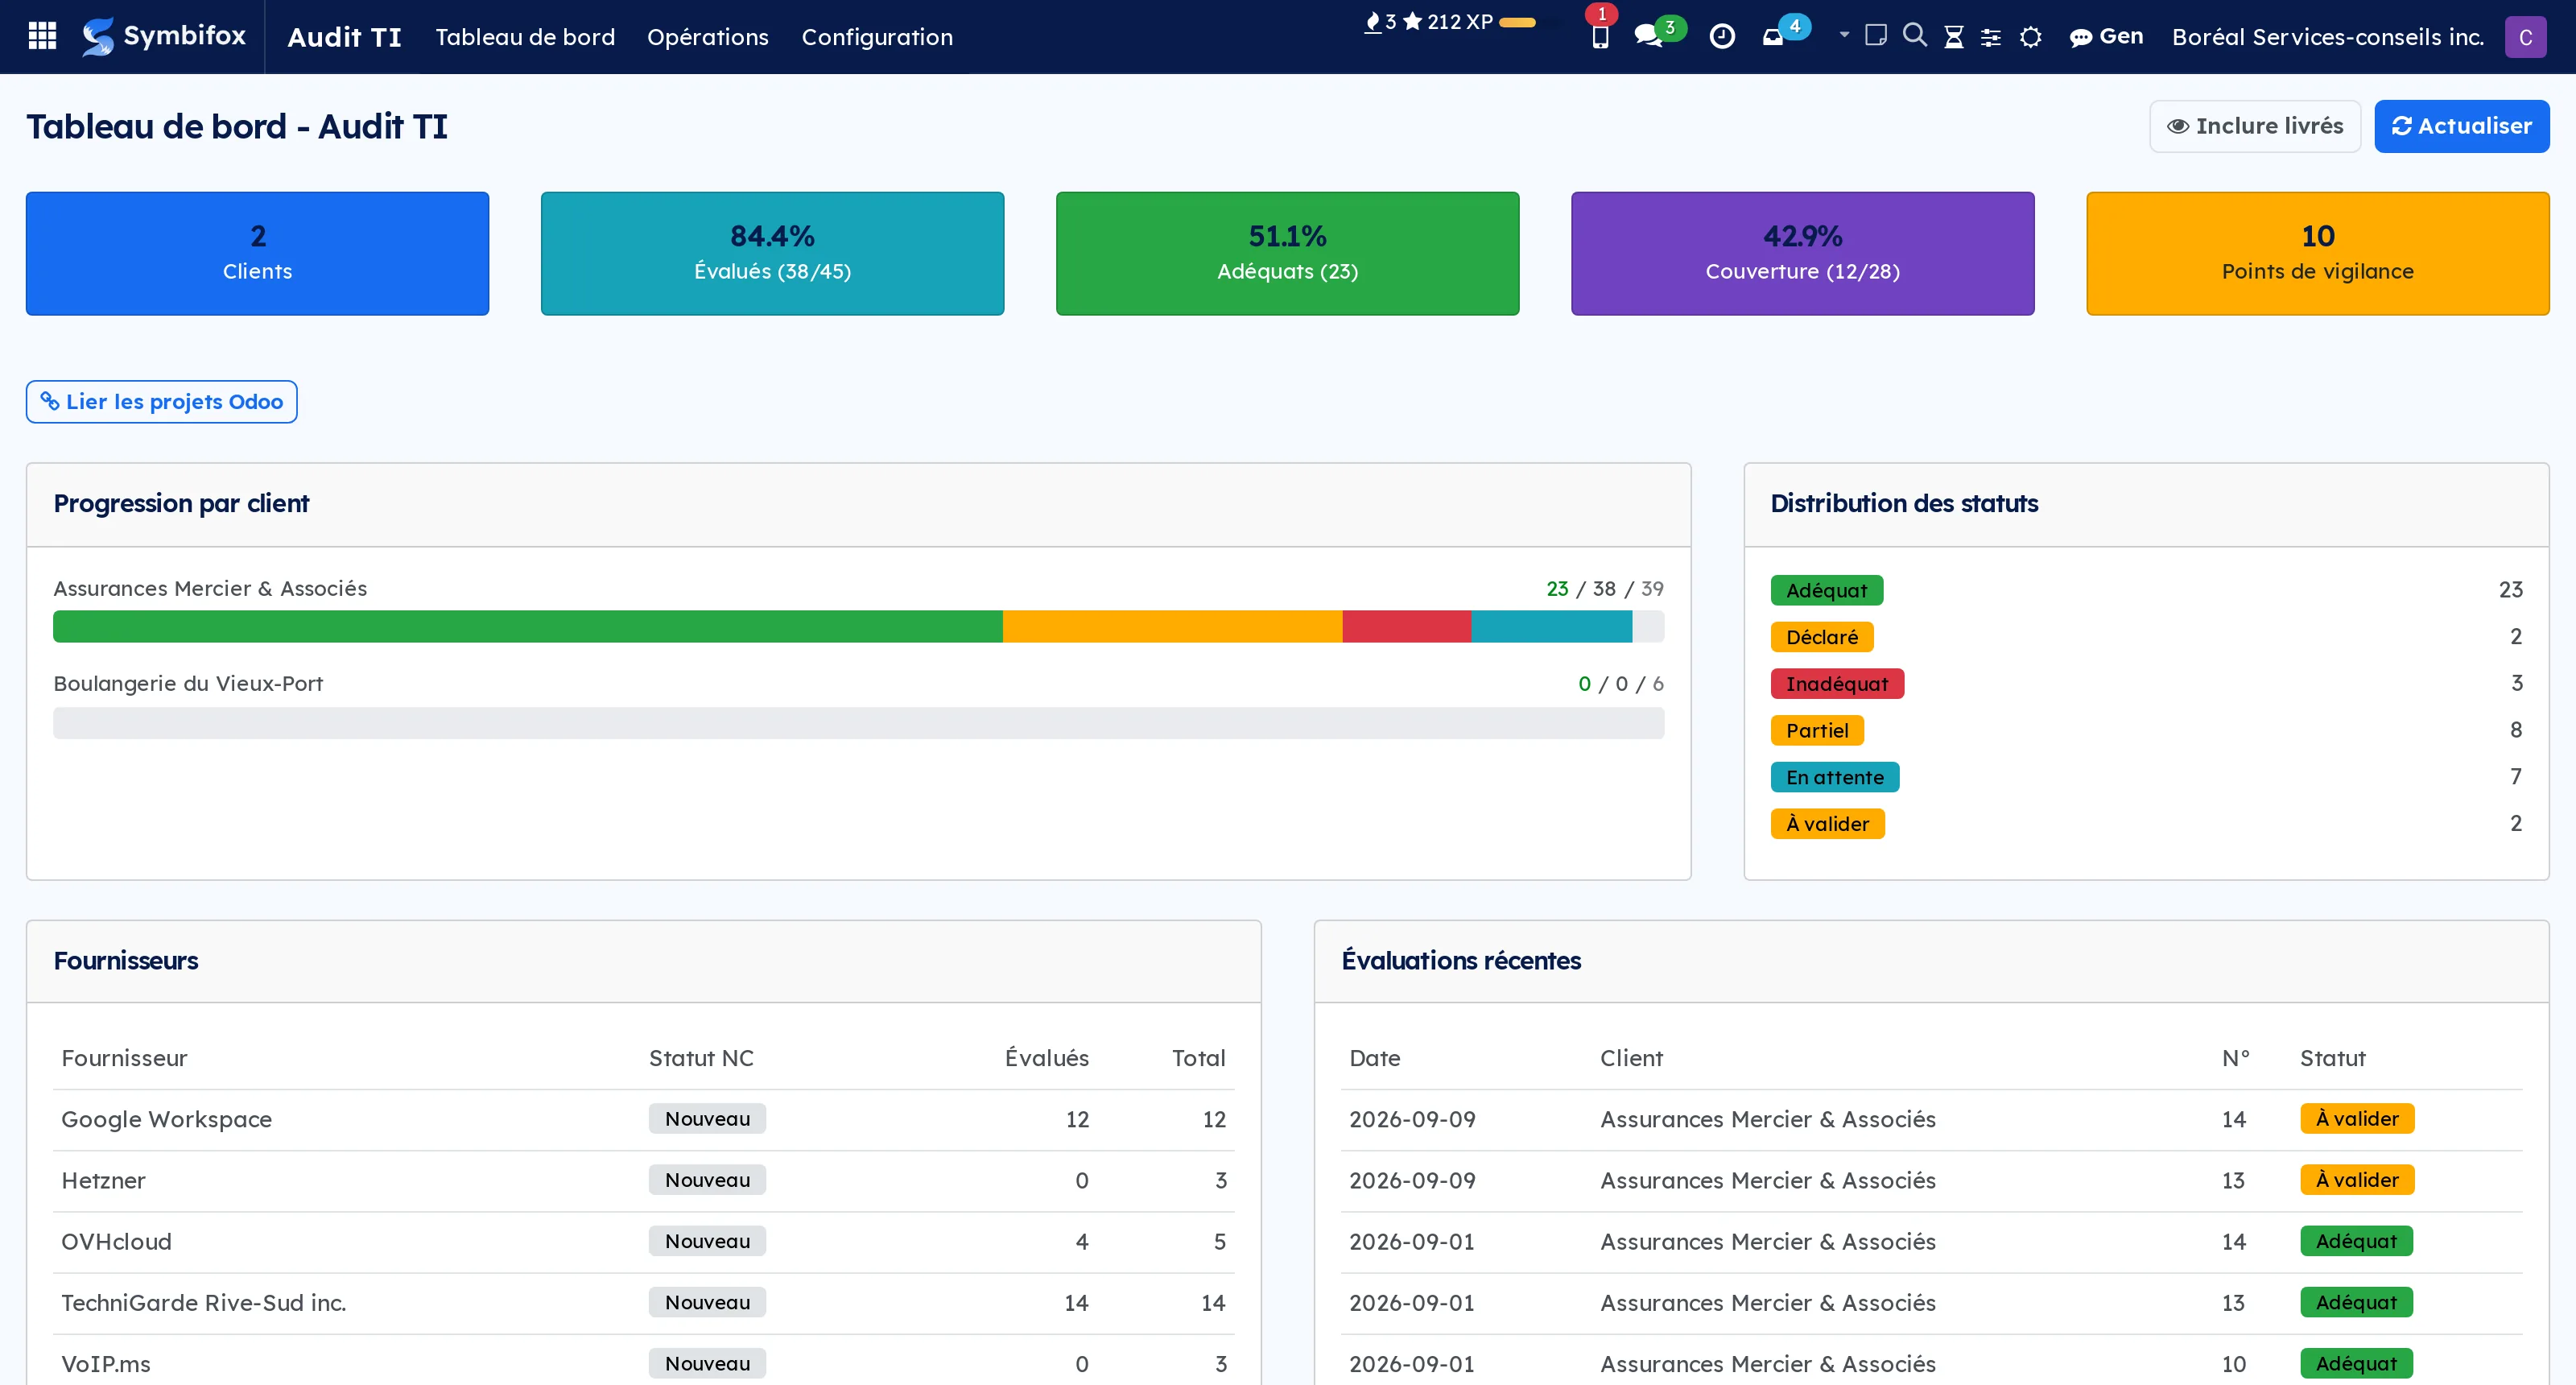
An IT audit is easy to narrate and hard to prove. The question that comes back is not “do you have backups” but “which of your four providers holds them, and since when”.
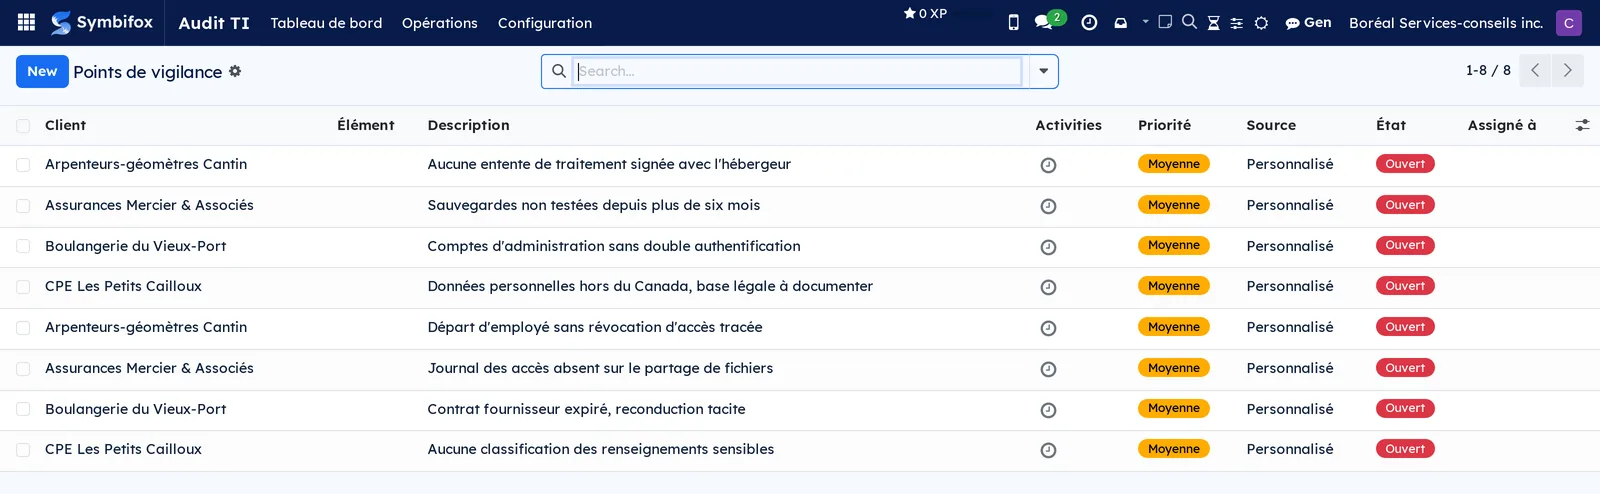
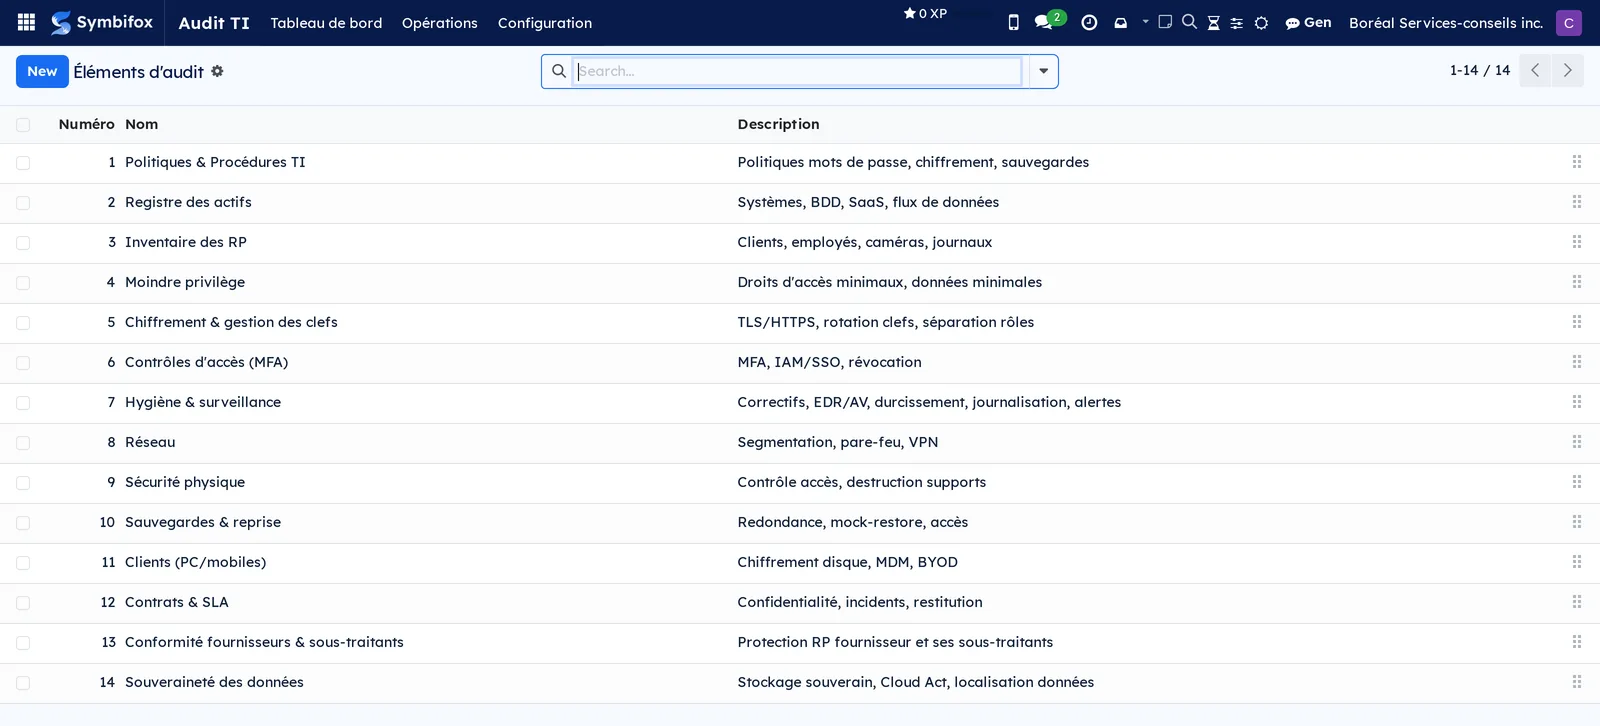
Five notions are enough. An audit element is a theme to check: fourteen ship with the module, from policies to backups. An IT provider is a third party that touches the audited organization's data. An audited client is the engagement file. An assessment is the crossing of a client, a provider and an element: it is the cell of the grid, and it carries a status. A watchpoint is a risk raised during the engagement, with its priority and the person responsible.
The crossing is what changes everything. Assessing an element without naming the provider that carries it produces a report you cannot hand to anyone to act on.
The dashboard sums up each engagement in three numbers, the green, yellow and red elements, without opening the file. Coverage sits next to the adequacy rate: an engagement at 100% adequate on 30% assessed is not a good engagement.
Co-developed with PME Conforme for Law 25 audits of Quebec small businesses and non-profits.
Comparable to Vanta or Drata, tailored to Law 25
Shall we look at your case together?
Tell us what you run today. We will tell you honestly whether Symbifox helps or not.
The catalog grows almost every month.
What gets added, what we learn deploying it, and nothing else. You leave whenever you want.
One confirmation email, and nothing before you follow its link. Then 10 welcome emails, one a week, then the updates. No tracker, no resale.