Privacy
Consent tracking and destruction register, multi-framework (Law 25, GDPR, PIPEDA…).
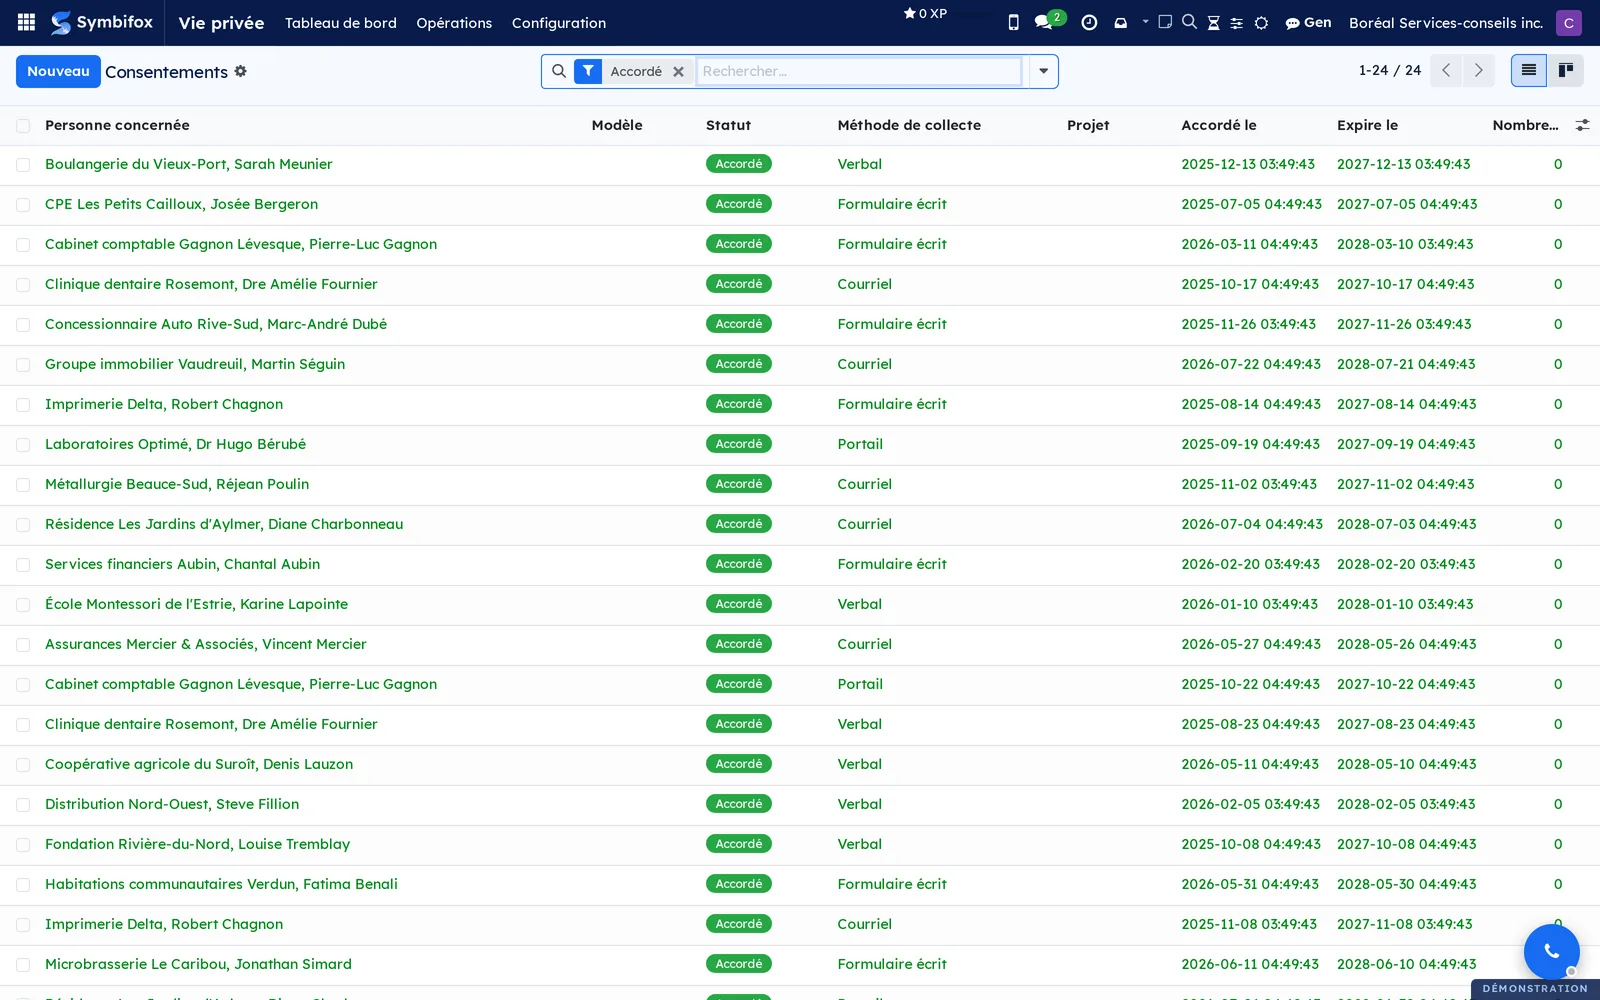
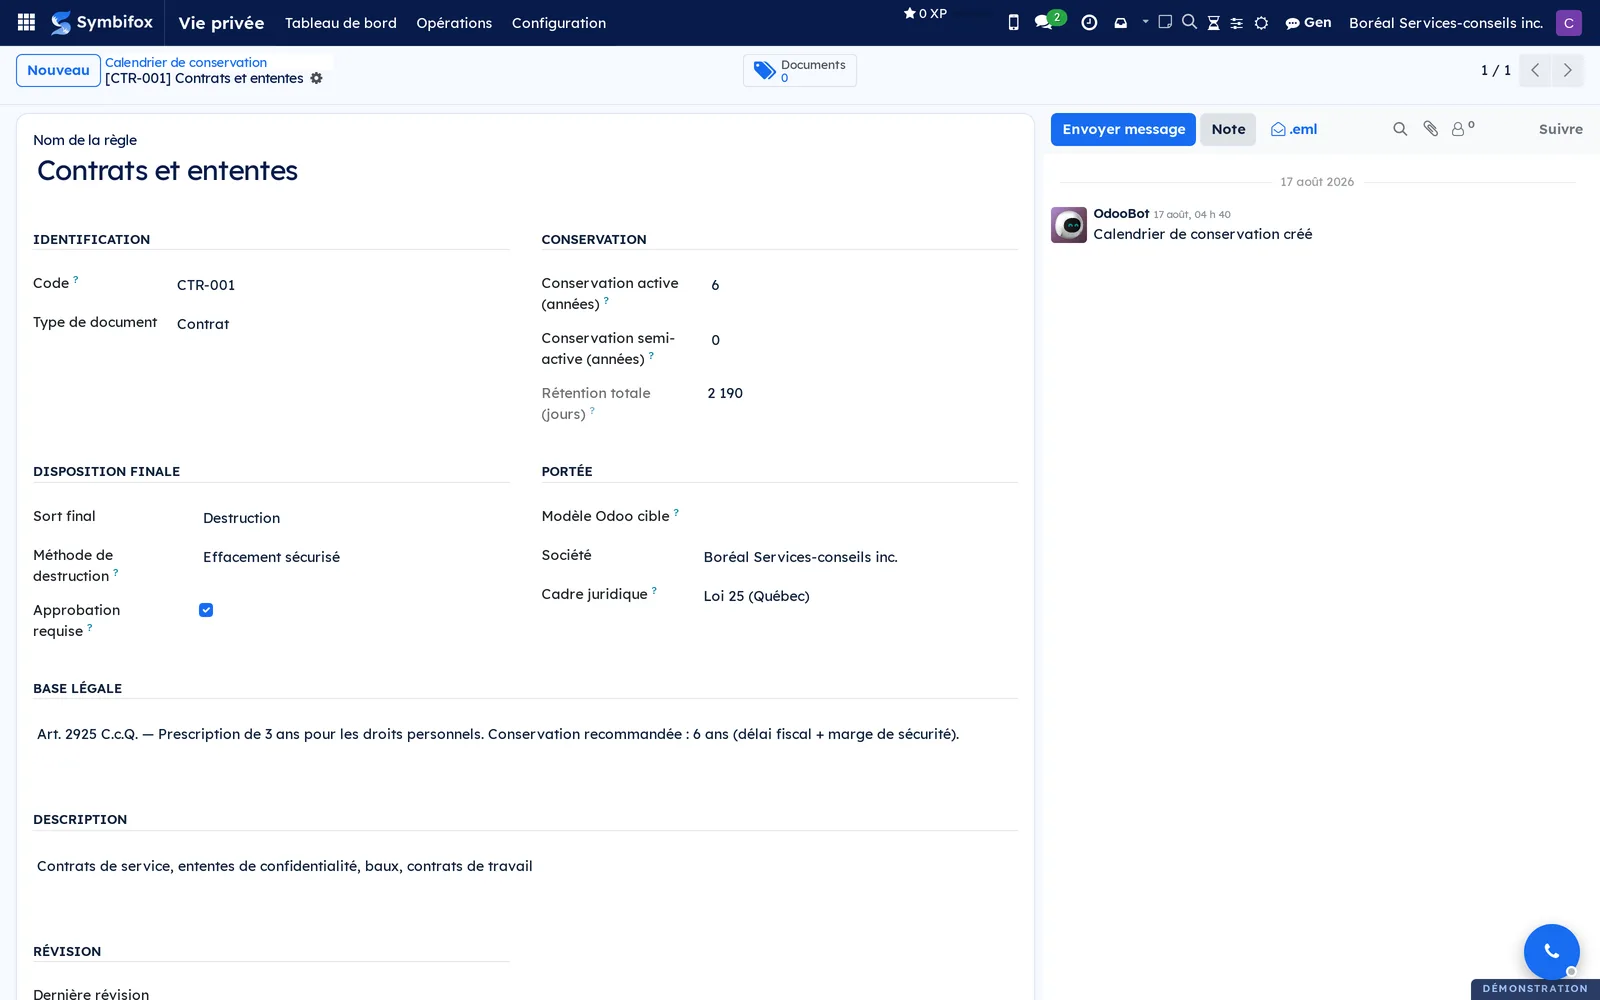
A consent you cannot reconstruct is not a consent. The question asked in an audit is not “did you ask” but “what exact text did the person accept, and when”.
A purpose says why you collect. A notice is the text presented to the person: it is versioned and each version carries a fingerprint, which lets you state later what was accepted. A consent links a person, a purpose, a notice version and evidence: signed file, capture, portal log.
Contact preferences say through which channel a person agrees to be reached, with a Do not contact switch that overrides everything else.
The documentary side follows the same logic: retention schedule, destruction register, incident register, handling of access requests.
⚠️ The engine is multi-framework. Quebec's Law 25 is built in; companion modules cover GDPR, UK GDPR, PIPEDA and New Zealand's Privacy Act 2020. Emails and certificates adapt to the applicable framework, because a response deadline and a definition of incident are not the same from one regime to the next.
Comparable to OneTrust or Didomi, small-business flavor
1 add-on module
Breach notices and incident registerNotify a client of a breach of its information, prove it was received, and keep the register Law 25 requires.
The service provider notifies its client's privacy officer: dated, versioned, with an acknowledgement that proves when, what and who.
Shall we look at your case together?
Tell us what you run today. We will tell you honestly whether Symbifox helps or not.
The catalog grows almost every month.
What gets added, what we learn deploying it, and nothing else. You leave whenever you want.
One confirmation email, and nothing before you follow its link. Then 10 welcome emails, one a week, then the updates. No tracker, no resale.